
Administrative Access
Administrative access is where a small mistake has the biggest blast radius. One person with organization-wide permissions they no longer need is a security incident waiting to happen, and one team without the access it needs is a blocked project. The goal of this step is an admin model that is secure, scalable and easy to change as people move around.
In the previous post you created managed users and the recommended admin groups. Now you decide what each of those groups is actually allowed to do.
Grant to groups, not to people
The core rule carries straight over from the last step: in Google Cloud, IAM roles are assigned to groups, and users are added to those groups. This keeps access consistent and avoids permission sprawl, the slow buildup of one-off grants that nobody can explain a year later.
Here is the concrete version. Instead of granting BigQuery roles directly to an analyst, you add the analyst to a data team group that already has the required roles. When that analyst moves to another team, you change their group membership. The IAM policy itself never needs to be touched.
That has three practical benefits. Access changes become a membership change instead of a policy edit, which lowers operational overhead. Auditing becomes easier, because you review a few group bindings instead of hundreds of individual ones. And least privilege becomes something you can actually maintain, because each group is scoped to a job function rather than to whatever a particular person once asked for.
The common admin groups
At the organization level, a standard set of admin groups is a good starting point. You can extend or customize it, but most organizations need something close to this.
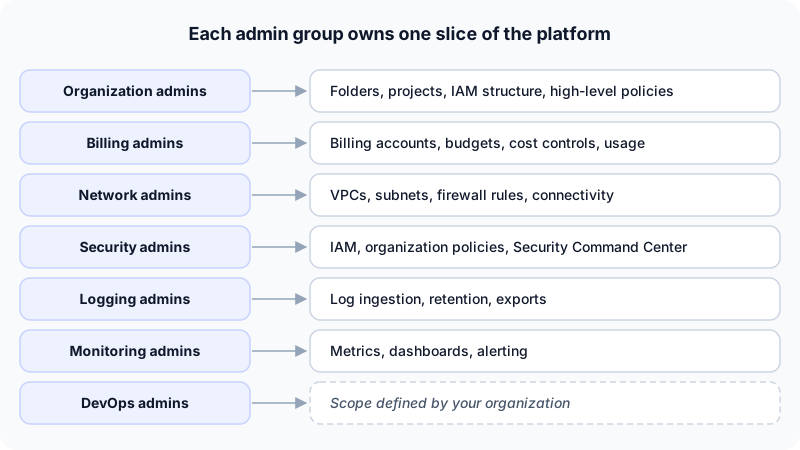 Each admin group maps to one area of responsibility
Organization admins manage the overall structure of the environment: folders, projects, the IAM structure and high-level policies. They shape the skeleton that every other team works inside.
Billing admins manage billing accounts, budgets, cost controls and usage visibility across the organization. Keeping this separate means the people who watch spend do not also need the power to change infrastructure.
Network admins manage VPCs, subnets, firewall rules and connectivity between environments. Networking is shared by everyone, so it benefits from a single accountable owner.
Security admins manage IAM permissions, organization policies and security services such as Security Command Center. They define the guardrails the other groups operate within.
Logging admins manage log ingestion, retention and exports, while monitoring admins manage metrics, dashboards and alerting. Splitting the two lets you control who can change what is recorded separately from who can change what is watched.
DevOps admins round out the common set. Their exact scope varies more than the others, so define it explicitly for your organization rather than assuming a default.
Assigning the roles
Administrative access is typically configured with the Setup your Foundation workflow in the Google Cloud Console. For each admin group, you select the group, assign the recommended IAM roles, apply any optional role customizations, then save and review the configuration. Repeating that same sequence for every group is what keeps role assignments consistent.
The recommended roles are a sensible default, so start there and customize only when you have a concrete reason. Every customization is something you will need to explain and maintain later.
Design decisions to make up front
The workflow handles the mechanics, but a few decisions are yours, and they are easier to make before granting anything than after.
First, decide which admin groups you need at each level: organization, folder and project. Not every group belongs at the organization level. A team that only operates one environment probably needs its admin rights on that environment's folder, not across the whole organization.
Second, decide who belongs in each group based on job function, not seniority or convenience. Imagine the finance group needs to see spend across all projects. They belong in billing admins. They do not need organization admin just because it would also let them see costs.
Third, decide how you balance least privilege with operational efficiency. Too tight, and teams spend their days waiting for access. Too loose, and you are back to permission sprawl. Clear ownership and well-defined roles are what make that balance workable day to day.
Watch out: Remember from Cloud Identity and Organization that Super Admins automatically have organization-level permissions, and that the initial Super Admin is added to every admin group by default. Once real owners are in place, review that membership instead of leaving it as is.
Verifying the result
After configuration, verify administrative access by reviewing the IAM section at the organization level. You are checking three things: that all the required groups exist, that each one has the correct roles, and that no individual users hold unnecessary elevated permissions.
That last check is the one most often missed. If you prefer the command line, you can list organization-level bindings that point at individual users rather than groups:
gcloud organizations get-iam-policy ORGANIZATION_ID \
  --flatten="bindings[].members" \
  --filter="bindings.members:user:" \
  --format="table(bindings.role, bindings.members)"
Ideally this returns very little. Anything that does show up deserves a question: should this person be in a group instead?
Wrapping up
A good administrative access model comes down to one habit, granting roles to groups rather than people, applied through a clear set of admin groups that each own one area of the platform. Decide where each group's access applies and who belongs in it, assign the recommended roles consistently, and verify that no individual is quietly holding elevated rights. The payoff is strong governance, simpler access management and the flexibility to grow on Google Cloud without the access model falling apart. With identity, groups and admin access in place, the next step is the resource hierarchy those groups will manage.