
Users and Groups
Once Cloud Identity is running, the next question is who goes into it and how they are organized. A messy user and group model is one of the most common reasons access control becomes unmanageable: permissions get granted person by person, nobody remembers why, and offboarding turns into an archaeology project. This post covers how to bring users in, how to deal with accounts that already exist, and how to structure groups so access scales.
It builds on the previous step in this series, Cloud Identity and Organization, and assumes you already have Cloud Identity set up, your domain verified and your Google Cloud organization created.
Why managed users
Google Cloud uses Cloud Identity to manage users and groups centrally. A managed user is an account created and controlled inside Cloud Identity, which means the organization, not the individual, decides how that account behaves. That gives you:
- Centralized user lifecycle management
- Single sign-on support
- Enforced two-step verification
- Audit and security reporting
- API-based administration
The alternative is a Google consumer account: a personal Google account that someone created themselves, often using their corporate email address. The organization does not control it, cannot enforce policies on it and cannot reliably remove it when the person leaves. That is why the best practice is simple: use Cloud Identity managed accounts for everyone who works in your environment, and avoid consumer accounts for enterprise use.
Getting users into Cloud Identity
How you provision users depends mostly on how many you have and where they already live.
Manual creation in the Admin Console is the simplest path. It works for a handful of administrators or a small team, but it does not scale: every new hire is a manual task and a chance for inconsistency.
Bulk upload with a CSV file is useful for initial migrations or for onboarding a large team at once. It is still a point-in-time operation, though, so it does not keep users in sync afterwards.
Directory synchronization is the answer for organizations that already have a directory. If you run LDAP or Active Directory on premises, Google Cloud Directory Sync performs one-way synchronization, keeping your existing directory as the source of truth. A cloud-based Directory Sync service is also available, and third-party identity providers such as Azure AD or Okta are supported.
The one-way direction is a feature, not a limitation. Imagine HR disables an employee's account in Active Directory on their last day. With synchronization in place, that change flows into Cloud Identity without anyone remembering to do it twice.
Conflict accounts
There is one trap that catches almost every organization during this step. A conflict account occurs when someone already has a personal Google account using the same email address the organization now wants to manage.
Engineer: Why can't I just sign in? I've used this Google account with my work email for years.
Admin: Because that account is personal. We need your work address to be a managed account, so you'll either transfer it to us or rename the personal one.
Conflicts should be resolved before you create the managed users. You have two options. You can invite users to transfer their account into a managed account, or you can force the conflict, which requires the user to choose a new email address for their personal account. The Transfer Tool for unmanaged users in the Admin Console helps you find and resolve these conflicts.
Tip: Talk to affected users before you take action. A short heads-up explaining why the change is happening and what they need to do avoids confusion and support tickets.
Once existing conflicts are cleaned up, you want to stop new ones from appearing. Two measures help: proactively create managed users in Cloud Identity before people have a reason to create personal accounts, and block Google consumer account verification emails at your email provider. Together they make sure every account with your domain is created and managed centrally.
Groups: the unit of access
With users in place, the most important design decision is this: assign roles to groups, never to individual users, and put users into groups.
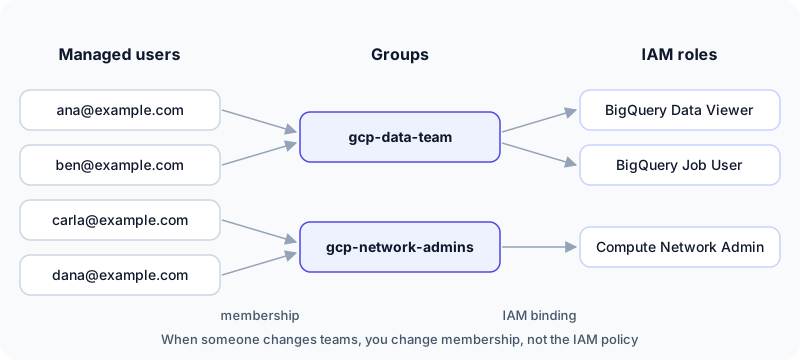 Users get access through group membership, never through direct role grants
Say a team of 30 engineers needs access across a dozen projects. If roles are granted per person, every hire, transfer and departure means editing IAM policies in many places, and sooner or later someone keeps access they should have lost. With groups, the IAM policy is written once against the group, and day-to-day changes are just membership changes. That is less work, fewer mistakes and a much easier audit.
Google provides a set of recommended admin groups to start from, which you can create with the Setup your Foundation workflow in the Google Cloud Console. They include organization admins, billing admins, security admins, network admins, monitoring admins and logging admins. Each one represents a job function, which is exactly what role-based access control and least privilege need.
The workflow itself is straightforward: create the recommended admin groups, verify in the Google Cloud Console that they were created, then add users to the appropriate groups. By default, the initial Super Admin is added to all of the groups, and you can add more members as needed. That default gets you started, but it is worth revisiting once the real owners of each function are in place.
Wrapping up
This step turns an empty identity platform into a structured access model. Managed users give the organization control over every account, directory synchronization keeps them current without manual work, and resolving conflict accounts early prevents personal accounts from lingering on your domain. Most importantly, groups become the unit of access: users join groups, groups hold roles. That model reduces operational overhead, improves auditability and sets up consistent IAM across your environments. The next post takes those admin groups and decides exactly what each one is allowed to do.