
Organizational Security
Most cloud security problems are not exotic attacks. They are a virtual machine that got a public IP because nobody said it shouldn't, a bucket shared with a personal Gmail account, or a default network with SSH open to the world. Organizational security in Google Cloud is about making those mistakes hard to make in the first place, and noticing quickly when something slips through. It works best when you set it up early and apply it consistently, before hundreds of projects exist and every exception has an owner who will argue for it.
Two building blocks do most of the work: organization policies, which prevent risky configurations, and Security Command Center, which shows you the risks and threats that exist anyway.
Guardrails and visibility: two halves of one job
It helps to think of organizational security as two complementary questions. The first is "what should never be allowed?" That is the job of organization policies. They are compliance guardrails that control how resources can be created and used, and they are enforced by the platform itself, regardless of what IAM permissions a user has.
The second question is "what is actually happening?" No set of guardrails is complete. People find new ways to misconfigure things, vulnerabilities are discovered in software you already run, and some threats only show up at runtime. Security Command Center answers this question by giving you a centralized view of security risks and threats across your Google Cloud environment, so you can prevent, detect, and respond to issues from one place.
You need both. Guardrails without visibility leave you blind to everything the rules did not anticipate. Visibility without guardrails means you spend your days cleaning up problems that a single policy could have prevented.
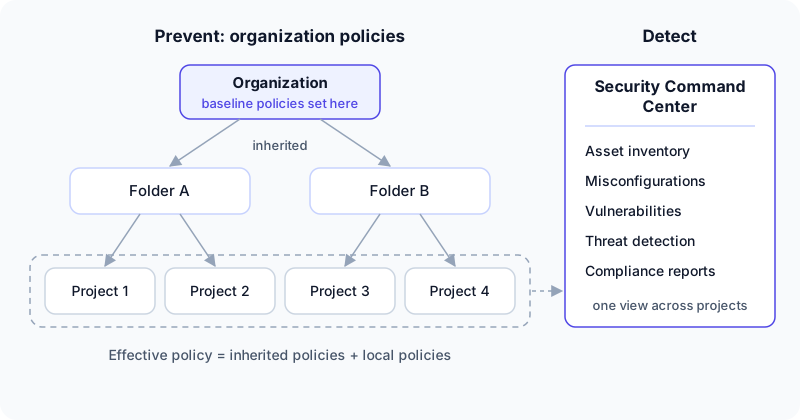 Organization policies are inherited down the hierarchy, and Security Command Center gives one view across all of it
How organization policies are applied
Organization policies can be attached at any level of the resource hierarchy you built earlier in this series: the organization, a folder, a subfolder, or an individual project.
Policies are inherited from the top down by default. The effective policy on a resource is the combination of what it inherits from its parents and what is defined on the resource itself. That has a practical consequence: a policy set at the organization node becomes the baseline for every folder and project, including ones that will be created next year by teams you have not hired yet. This is why the most important policies belong at the top. Setting them per project means relying on every new project being configured correctly, which is exactly the kind of manual step that eventually gets skipped.
Imagine a company with three business units, each with its own folder and a few dozen projects. If the platform team sets a policy at the organization level, all of those projects are covered on day one. If one business unit has a legitimate need to behave differently, that can be handled lower in the hierarchy as a deliberate, visible decision rather than an accident.
Three policies worth setting at the organization level
Some organization policies are strongly recommended at the organization level because they close common, high-impact gaps.
Disable external IP addresses on virtual machines. A VM with an external IP is directly reachable from the internet, which makes it part of your attack surface whether or not anyone intended that. Disabling external IPs by default pushes traffic through controlled, centrally managed paths and turns internet exposure into an explicit choice.
Domain restricted sharing. This policy ensures IAM access can only be granted to identities from approved domains. Without it, a single well-meaning engineer can share a project or dataset with an external or personal account, and that access may persist long after anyone remembers granting it. With it, the mistake simply cannot be made.
Skip default network creation. By default, a new project gets a network with subnets in every region and firewall rules that are more permissive than most organizations want, such as open SSH and RDP access. Skipping default network creation means projects start with no network at all, and teams use the shared, centrally designed networks instead.
Together these policies establish a strong security baseline. None of them is complicated, but each one removes a whole category of incidents.
Tip: Treat organization policies as a living part of your foundation, not a one-time setup. Managing them requires the Organization Policy Administrator IAM role, so keep that role with a small group and review the policies regularly against your security and compliance requirements.
Security Command Center
Security Command Center is where the "what is actually happening?" question gets answered. Its core capabilities cover four areas: an inventory of assets and resources across all your projects, detection of misconfigurations and vulnerabilities, threat detection (including malware and data exfiltration), and compliance reporting against industry benchmarks.
The inventory alone is valuable. In a growing organization, simply knowing what resources exist, and where, is hard. Misconfiguration detection then tells you which of those resources break good practice, and threat detection covers the runtime side, where something may be configured correctly but is still being abused. Compliance reporting ties it together by showing how your environment measures up against recognized benchmarks, which is useful both for internal reviews and for conversations with auditors.
Choosing a tier
Security Command Center comes in two tiers:
| Tier | Cost | What it adds |
|---|---|---|
| Standard | Included at no cost | Asset visibility and detection of high-risk misconfigurations |
| Premium | Paid | Advanced threat detection, compliance monitoring, and automated security insights |
Standard is a sensible starting point for any organization, since there is no reason not to have basic visibility. Premium becomes relevant when you need active threat detection and continuous compliance monitoring, for example when you run production workloads with regulatory requirements or sensitive data.
Making it part of the foundation
The easiest time to get this right is during foundation setup, before workloads arrive. A typical foundation setup enables the recommended organization policies, enables Security Command Center, and grants the required roles automatically as part of the process. Doing these steps together, as part of the same setup that creates your hierarchy and networks, gives you centralized visibility and consistent enforcement from the very first project.
Retrofitting is much harder. Turning on domain restricted sharing in an organization that already has external accounts scattered across projects means auditing and cleaning up each one first. Disabling external IPs after teams have built around them means migrations. Starting with the guardrails in place avoids all of that.
Wrapping up
Organizational security in Google Cloud rests on two complementary tools. Organization policies are inherited down the resource hierarchy and prevent risky configurations before they happen. Disabling external IPs, restricting sharing to approved domains, and skipping the default network are three strong baseline policies to set at the organization level. Security Command Center gives you a single view of assets, misconfigurations, vulnerabilities, threats, and compliance, starting with the free Standard tier and moving to Premium when you need deeper detection. Set both up early, as part of your foundation, and you get protection, visibility, and the confidence to scale securely.