
Network Management
Networking is the part of a cloud foundation that is hardest to change later. IP ranges, subnet layouts and the way projects connect tend to get baked into every workload, so a rushed decision on day one becomes a migration project in year two. The good news is that Google Cloud networking is built on a global private backbone connecting regions, zones and services worldwide, and once you understand a few concepts the right design choices become fairly obvious.
This post builds on the resource hierarchy from the previous part of the series, where you created a shared networking project. Here you will see what goes into it and why.
Network service tiers
The first decision is how traffic travels between your resources and your users. Google Cloud offers two network service tiers.
The Premium tier keeps traffic on Google's private infrastructure for as long as possible. Traffic enters Google's network close to the user and exits close to the destination, which gives better performance, lower latency and improved security, since less of the journey happens on the public internet.
The Standard tier leaves Google's network earlier, crosses the public internet, and re-enters closer to the destination. It is lower cost, but latency can be higher and performance less predictable.
Think of it as a trade between cost and consistency. A customer-facing API serving users on several continents benefits from Premium. An internal batch job that downloads a nightly file can tolerate the Standard tier without anyone noticing.
VPCs and subnets
A Virtual Private Cloud (VPC) in Google Cloud is a global resource. A single VPC can span multiple regions, and resources in different regions communicate using private IPs over Google's backbone. If you come from other clouds where a network is tied to one region, this is the biggest mental shift: you do not need one network per region and a mesh of connections between them.
Subnets, on the other hand, are regional. Each subnet lives in one region and has its own IP range. Even so, resources in different subnets and regions can still talk to each other privately, because they share the same VPC.
When you create a VPC you choose a subnet mode. In auto mode, Google Cloud automatically creates a subnet in every region with predefined IP ranges and firewall rules. It is convenient for experiments but not recommended for production: you do not control the ranges, which makes overlaps with on-premises networks or other VPCs likely, and you get subnets in regions you may never use. In custom mode, you decide the IP ranges, the regions and the firewall rules. Custom mode is strongly recommended for production, and it is the only sensible choice if you plan to connect to other networks, as the next post in this series does.
Private Google Access
Many workloads have no reason to be reachable from the internet, but they still need Google APIs and services such as Cloud Storage or BigQuery. Private Google Access lets resources without external IP addresses reach those APIs and services. The traffic stays on Google's network and never traverses the public internet.
This is what makes "no external IPs" a realistic policy instead of a wish. A data processing VM can read from a bucket and write to BigQuery while having no public address at all, which removes an entire class of exposure.
Connecting networks: Shared VPC, peering and Cloud VPN
By default, VPCs are isolated from each other. When workloads in different networks need to talk, you have several options, and they solve different problems.
Shared VPC lets a centrally managed host project provide networking resources to multiple service projects. The network team owns the VPC, subnets, firewall rules and connectivity in the host project, and application teams deploy their workloads into the shared subnets from their own service projects. This is separation of duties applied to networking, and it fits naturally with the network admins group from the administrative access post.
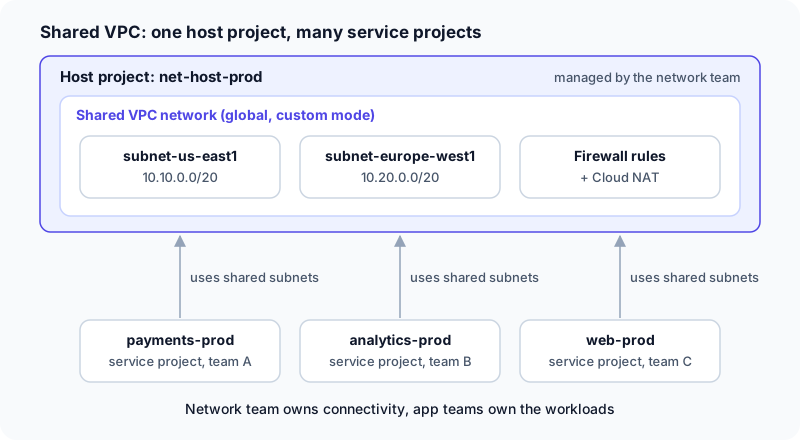 Shared VPC: the network team manages one host project, and application teams deploy into its subnets
Imagine thirty engineers across four product teams, each with their own projects. Without Shared VPC, each team builds its own network, picks its own ranges, and writes its own firewall rules, and someone eventually has to connect them all. With Shared VPC, there is one network, one place to review firewall rules, and one set of IP ranges to keep consistent. Shared VPC improves governance, simplifies network management and reduces duplication.
VPC peering connects two VPCs using private IP connectivity. Peering is non-transitive: if network A peers with B, and B peers with C, A cannot reach C through B. Peering uses standard network pricing. It works well for a small number of networks that need direct private connectivity, but it gets awkward as the number of networks grows.
Cloud VPN provides encrypted connectivity between VPCs, or between Google Cloud and on-premises environments. It is suitable for hybrid connectivity when low latency is not a strict requirement. It gets a full post of its own next in this series.
| Option | What it connects | Good fit |
|---|---|---|
| Shared VPC | Many service projects to one host project's network | Central network team, many application teams |
| VPC peering | Two VPCs, privately, non-transitive | A few networks that need direct private links |
| Cloud VPN | VPCs or on-premises, encrypted | Hybrid setups without strict latency needs |
Best practices that hold up
Most good Google Cloud network designs share the same handful of habits:
- Use custom mode VPCs for greater control.
- Centralize networking using Shared VPC.
- Use fewer, larger subnets to simplify management.
- Avoid assigning external IP addresses where possible.
- Enable Private Google Access for private workloads.
Each one reduces either complexity or exposure. Fewer, larger subnets mean fewer ranges to track and fewer firewall rules tied to specific ranges. Avoiding external IPs, backed by Private Google Access, means most of your workloads simply have nothing listening on the internet.
Watch out: IP ranges are the decision you are least able to undo. Before creating subnets, write down the ranges used on-premises and in any other cloud you might connect to, and make sure your plan does not overlap them.
Networking in the foundation setup
The Setup your Foundation workflow covers networking too. It lets you configure multiple VPCs for different environments, such as production and non-production, and define their regions, IP ranges, firewall rules and optional Cloud NAT. You can review and validate the network architecture before deployment, which is the right moment to check it against your security and connectivity requirements rather than after workloads are running.
Wrapping up
Google Cloud networking starts from a global backbone and global VPCs, with regional subnets underneath. Choose the service tier based on how much consistent performance is worth to each workload. Use custom mode so you own your IP ranges, keep workloads off the public internet with Private Google Access, and centralize the network in a Shared VPC host project so one team can govern it while others build on it. Peering and Cloud VPN fill the gaps between networks, and when one of those networks lives outside Google Cloud, you are in the territory of the next post: hybrid connectivity.