
Cloud Identity and Organization
Before you deploy a single workload on Google Cloud, you need to answer two questions: who are your users, and what are they allowed to do? If those answers live in the same place and are managed by the same people, access control gets tangled quickly. This post covers the first foundation step from the onboarding overview: setting up Cloud Identity and the Google Cloud organization so that identity and authorization stay cleanly separated from day one.
The three pillars of access control
Google Cloud access control rests on three pillars, each answering a different question and each handled by a different service.
| Pillar | Question it answers | Handled by |
|---|---|---|
| Authentication | Who is this user? | Cloud Identity |
| Authorization | What is this user allowed to do? | Cloud IAM |
| Auditing | Who did what, and when? | Cloud Operations |
Authentication verifies identity and controls how users sign in to Google Cloud services. Authorization assigns roles and permissions to authenticated identities. Auditing records actions across the environment so you can reconstruct what happened later.
The split is useful because each pillar can change independently. Say an engineer moves from the data team to the platform team. Their identity does not change, only what they are authorized to do. And the audit trail of what they did before the move stays intact. When these concerns are mixed together, a simple team change turns into a risky edit of several systems at once.
What Cloud Identity is
Cloud Identity is the centralized identity platform for Google Cloud and Google Workspace. It is where you manage users and groups, and where you integrate third-party identity providers using standards such as SAML or LDAP.
Its most important design property is that it separates identity management from resource authorization. Cloud Identity knows who your people are and how they are grouped. It does not decide which projects they can touch. That is IAM's job, inside the Google Cloud organization. Keeping the two apart simplifies access control and improves security, because each side can be managed by the people best placed to manage it.
Domains: the root of your identity
Everything in Cloud Identity hangs off domains, and there are three kinds worth understanding before you start.
| Domain type | What it is for | Can users sign in with it? |
|---|---|---|
| Primary domain | The main company domain, which becomes the organization name and the root identity boundary | Yes |
| Domain alias | Additional domains used for email only, with no separate identity space | No |
| Secondary domain | Subsidiaries or child companies, where users and groups can be created | Yes |
Imagine a company that owns example.com, uses example.net only as an alternate email address, and recently acquired a subsidiary that runs on example-labs.com. The first is the primary domain, the second is an alias, and the third is a secondary domain. Getting this right matters because the primary domain becomes the name of your Google Cloud organization, and that is not something you want to revisit later.
Two consoles, two kinds of administrator
Identity and access are managed from two different consoles, and the split mirrors the pillars above.
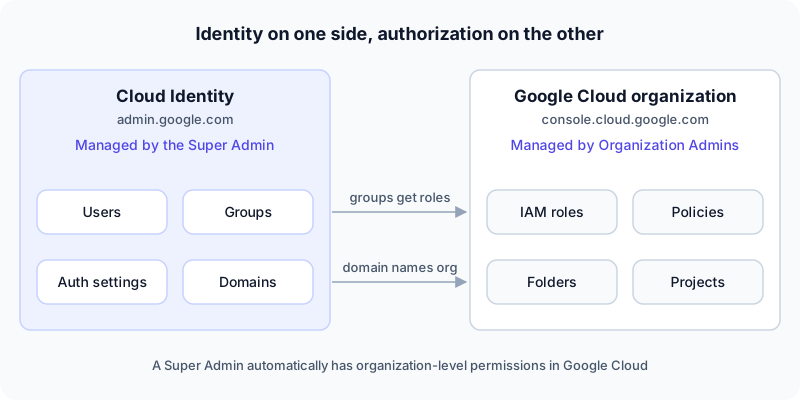 Cloud Identity handles who users are, the organization handles what they can do
The Cloud Identity Admin Console at admin.google.com is managed by the Super Admin. Super Admins are responsible for identity and authentication: users, groups, domains, authentication settings and other security settings in Cloud Identity.
The Google Cloud Console at console.cloud.google.com is managed by Organization Admins. They are responsible for authorization: IAM roles, policies, folders and projects in Google Cloud.
This separation of duties enforces least privilege and reduces the risk of over-privileged accounts. The person who can create a user is not automatically the person who decides what that user can do in production.
Watch out: A Cloud Identity Super Admin automatically has organization-level permissions in Google Cloud. Treat Super Admin accounts as break-glass accounts: keep very few of them, protect them carefully, and do not use them for everyday work.
Setting it up
The setup flow is short, but the order is important.
First comes the initial setup: you provide business information and contact details, select the primary domain, and create the first Super Admin account.
Next is domain verification. You prove you own the primary domain by adding a TXT record to the domain's DNS configuration. The record looks something like this, with the value provided during setup:
example.com. 3600 IN TXT "google-site-verification=<value-from-setup>"
Once verified, the domain is protected and can be used to create managed users. This is also why the onboarding process checks DNS access during preparation: without someone who can edit DNS, setup stops here.
Finally, you can create users and groups from the Admin Console. Those groups are later mapped to IAM roles in Google Cloud, which is how access is managed at scale. That mapping is the subject of the next two posts.
Additional domains are added from the Admin Console too. Secondary domains and domain aliases must each be verified with DNS TXT records before they become active, and once a secondary domain is verified, you can create users and groups under it. This is how organizations with subsidiaries or several brands support a more complex identity structure while keeping control centralized.
Wrapping up
Cloud Identity and the Google Cloud organization are two halves of one design. Cloud Identity, run by Super Admins in the Admin Console, answers who your users are, anchored on a verified primary domain that also names your organization. The organization, run by Organization Admins in the Cloud Console, answers what those users can do. Keeping identity and authorization separate gives you centralized user management, scalable group-based access and a solid base for governance, and setting it up correctly now prevents painful access problems later. With the identity platform in place, the next step is filling it with the right users and groups.
Google Cloud Onboarding Series
- Technical Onboarding Center
- Cloud Identity and Organization (current)
- Users and Groups
- Administrative Access
- Resource Hierarchy
- Network Management
- Hybrid Connectivity
- Logging and Monitoring
- Organizational Security
- Customer Care Portfolio