
Designing a Resource Hierarchy
Every Google Cloud environment ends up with some kind of structure. The only question is whether you design it or whether it happens to you. Without a deliberate resource hierarchy you get isolated projects, access policies that differ for no good reason, poor visibility into what exists, and billing that nobody can explain. A well-designed hierarchy is what lets governance, security and cost tracking keep up as the environment grows.
In the previous posts of this series you set up Cloud Identity, created users and groups, and defined administrative groups. The hierarchy is where those groups finally get attached to something.
Resource Manager: the service behind the structure
The hierarchy is built and managed with Resource Manager. It does two jobs. First, it lets you organize cloud resources so they match how your company is actually structured and how teams work. Second, it gives you a central place to apply IAM policies and organization policies, so you set a rule once instead of repeating it in every project.
Resource Manager also enables centralized billing and usage reporting across projects. That matters more than it sounds: when the finance group asks what the data platform cost last quarter, the answer should come from the structure itself, not from a spreadsheet someone maintains by hand.
Organization, folders and projects
The hierarchy is made of three kinds of containers, and each one has a clear role.
The organization is the root node. It represents the company and is created when you verify a domain with Cloud Identity, which is exactly what happened in part 2 of this series. Every folder and project lives under it.
Folders group projects logically. Their real value is that IAM and organization policies applied to a folder reach every project inside it, so you can treat "all of production" or "everything the payments team owns" as a single unit. Folders commonly represent teams, environments or business units, and they can be nested.
Projects are where the actual resources live: virtual machines, databases, storage buckets. A project is the primary boundary for IAM enforcement and for enabling services. If you need to answer "who can touch this database?" the project is where you start looking.
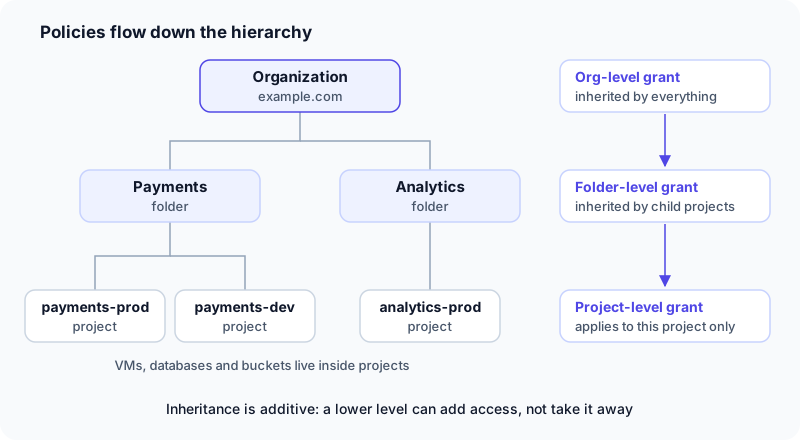 Grants flow down: organization to folders, folders to projects, projects to nothing below them
How IAM inheritance works
IAM policies follow a top-down inheritance model. A policy applied at the organization level is inherited by every folder and project. A policy applied at a folder is inherited by its child folders and projects. A policy applied at a project applies only to that project.
The important detail is that inheritance is additive only. Permissions granted at a parent level cannot be denied at a lower level. A child can receive more access than its parent gives, never less.
This single rule should shape most of your decisions. Imagine you grant a broad role to an engineering group at the organization level because it was quick. Six months later you create a folder for a regulated workload and want that group kept out. You cannot fix it in the folder. You have to remove the grant at the top and re-grant it everywhere else it was needed. The safe habit is the opposite: grant narrowly and as low in the tree as makes sense, and only move a grant upward when it truly applies to everything below.
Tip: Combine inheritance with the group-based model from the previous post. Granting a role to a group on a folder is one binding that covers dozens of projects, and changing who has access is just a group membership change.
Choosing a hierarchy pattern
There is no single correct hierarchy. The right one depends on how you manage teams, environments and billing. Three patterns cover most organizations, and the main difference is which dimension sits at the top.
| Pattern | Levels under the organization | Works well when |
|---|---|---|
| Team oriented | Teams → Environments → Projects | Teams own their environments and billing is shared |
| Business unit oriented | Business units → Teams → Environments → Projects | Billing and ownership must be separated by business unit |
| Environment oriented | Environments → Business units or teams → Projects | Strong environment isolation is required |
Whatever sits highest is the easiest to govern as a block. In an environment-oriented layout, a single policy on the production folder covers every team's production projects, which is great for isolation. The trade-off is that a team's resources are now spread across several folders, so anything specific to that team has to be granted in each environment. A team-oriented layout flips that: team ownership is simple, but enforcing a production-wide rule means touching every team folder.
To choose, ask four questions: how your teams are structured, how environments are separated, how billing should be tracked, and where policies need to be enforced. The best answer is the one that minimizes duplication, keeps access management simple, and still makes sense when the company is twice its current size. Say a company has three business units with separate budgets: the business unit pattern lets each unit's costs and owners line up with a single folder, which beats reconstructing it from project labels later.
Provisioning with Setup your Foundation
You do not have to build the hierarchy by hand. The Setup your Foundation workflow in the Google Cloud Console helps you visualize and deploy it. It lets you preview the hierarchy before anything is created, customize team and environment names, create shared projects for networking, logging and monitoring, and assign IAM roles to groups at folder and project levels.
Those shared projects are worth noticing, because they set up the next posts in this series: the networking project will host your Shared VPC, and the logging and monitoring projects will receive centralized logs and metrics.
Configurations can be saved and reviewed before deployment, and you can deploy them either through the console or with Terraform. Terraform is the better long-term choice if you want the hierarchy versioned and reviewed like any other code.
Deploying and validating
Provisioning typically takes around thirty minutes. Once it finishes, do not assume it is right. Check it. Review the folders and projects in Resource Manager to confirm the structure matches your design. Verify the IAM role bindings at each level, paying special attention to anything granted at the organization, since that is inherited everywhere. Finally, confirm that billing and policy inheritance behave the way you expect, for example by checking that a project in a production folder shows the policies set on that folder.
Watch out: An organization-level binding that "just needed to work for a demo" is the most expensive mistake to undo later, because every project in the company inherits it.
Wrapping up
The resource hierarchy is the skeleton of your Google Cloud environment. The organization is the root, folders group projects so policies can be applied once, and projects hold the resources and enforce access. Because IAM inheritance is additive, where you place a grant matters as much as what you grant, so keep broad roles out of the top of the tree. Pick the pattern whose top level matches the boundary you most need to enforce, provision it with Setup your Foundation or Terraform, and validate it before teams start deploying. With that structure in place, the next step is giving those projects a network.